
Quick answer
A certificate must cover the hostname visitors use and be served by the system receiving their connection. Check both the browser-facing endpoint and the hosting origin when a proxy is involved. Certificate issuance also depends on valid domain control and reachable validation paths.
Before you start
Identify the exact failing hostname, browser error, current DNS destination, and whether a proxy such as Cloudflare is in front of the host. Use the account's current SSL/TLS or certificate interface; labels vary by cPanel version.
What to do
- Confirm that DNS and the hosting domain mapping point to the intended account, including root and www as needed.
- Inspect the certificate names, expiry, chain, and relevant validation errors through the available certificate tools.
- Check CAA, proxy behavior, redirects, and validation access before requesting or rerunning certificate issuance.
- After issuance, test the real HTTPS URL and representative assets. Resolve mixed-content links in the application rather than disabling browser protections.
Check the result
Verify the certificate actually presented to visitors and confirm HTTP-to-HTTPS behavior. When a proxy is used, verify secure origin connectivity separately.
If something does not work
Never click through a certificate warning for normal use or publish private certificate keys as evidence. Send support the hostname and sanitized error, and keep existing working certificates until a replacement is confirmed.
SSL certificate expired or website not secure
Read the browser's exact error and hostname. An expired certificate, a hostname mismatch, an incomplete chain, an HTTP page and mixed-content assets are different problems. If a CDN fronts the website, the certificate shown to the browser can differ from the hosting origin's certificate.
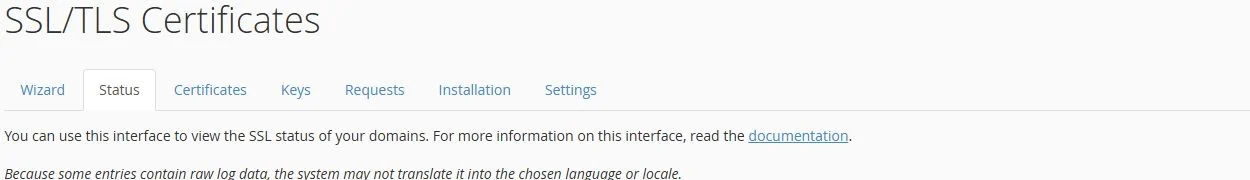
- Open the intended domain through its authorized cPanel account. In an interface with Security > SSL/TLS Certificates, select its Status tab for the available domain status controls. Older interfaces may list SSL/TLS Status separately. Review the covered domains and any available AutoSSL result; controls depend on your account permissions. Certificate-management and AutoSSL controls depend on account permissions.
- For a failed renewal/validation, compare the exact hostname's DNS destination, relevant CAA restrictions, validation path and redirects. A domain listed in cPanel does not establish that public DNS sends it there.
- For mixed content on an otherwise valid HTTPS page, identify the specific insecure asset in the browser's developer tools and correct its application URL or source. Reissuing the same certificate does not rewrite HTTP image/script links.
- After the authorized correction, reopen the exact HTTPS hostname and a representative page/asset. Check the served certificate dates/names and intended redirects. A successful issuance status does not alone prove that visitors reach that endpoint.
Do not send a private key, click through a certificate warning as a permanent workaround, or weaken CDN-to-origin encryption. Provide support with the hostname, browser error, relevant AutoSSL validation message and time/time zone.
cPanel screenshot example
View larger screenshot
In this cPanel Jupiter interface, open SSL/TLS Certificates and select Status. Older interfaces may list SSL/TLS Status separately. Available controls depend on your account permissions.
Related help
- Investigate an HTTPS redirect loop without disabling encryption
- Find where your domain's DNS is managed before changing records
- Use website error logs to diagnose a failed request
- Send a website support request with useful troubleshooting details
Official references
Reviewed October 31, 2026. Interfaces, vendor availability, and account features can change. Check your current account before making changes.
Customer symptom and related-help review: November 1, 2026.
